 Services
 Technologies
 About
 Success


Canadia Bank
Canadia Bank: Building a Secure and Scalable Hybrid Cloud Foundation with AWS
Learn how Canadia Bank built a scalable hybrid cloud foundation with AWS, strengthening cloud governance, networking, security, and operations.
Industry
Financial Services
Technology
How Canadia Bank and Renova Cloud built a secure and scalable hybrid cloud foundation with AWS Landing Zone to support cloud adoption and future workload migration.
Building the Foundation for Cloud Transformation
For financial institutions, moving to the cloud requires more than simply migrating workloads. A secure and well-governed cloud foundation is essential to support compliance, operational resilience, cost visibility, and future scalability.
Canadia Bank embarked on its cloud transformation journey with Amazon Web Services (AWS) as its chosen cloud platform. To support this transformation, the Bank partnered with Renova Cloud to design and implement a secure and scalable AWS Landing Zone that could serve as the foundation for future cloud workloads while integrating with its existing on-premises environment.
The solution establishes centralized governance and security controls, standardized networking and identity management, automated account provisioning, and cost governance.
This foundation enables Canadia Bank to accelerate future workload migration and cloud-native development while maintaining alignment with security, compliance, and AWS best practices.
“Canadia Bank is embarking on a cloud transformation journey. To ensure this transition is secure, compliant, and sustainable, the first and most critical step is the implementation of an AWS Landing Zone – the foundation for all future cloud workloads.”
The Challenge: Building a Secure Foundation for Cloud Adoption
As Canadia Bank began its cloud adoption program, it needed an environment that could support future workloads while maintaining strong governance, security, and integration with its existing infrastructure.
The Bank faced several practical challenges.
1. Lack of centralized governance
Managing a growing cloud environment requires a structured multi-account architecture and centralized governance.
Canadia Bank needed a foundation that could establish consistent controls across its AWS environment.
2. Complex hybrid networking
The Bank needed to connect its AWS environment with existing on-premises infrastructure while maintaining secure and reliable internal connectivity.
3. Regulatory compliance and security
As a financial institution, security and compliance are critical requirements. The cloud environment needed policy-based security controls and standardized approaches to managing network traffic, access, and infrastructure.
4. Operational overhead
Without standardized provisioning and centralized management, creating and operating cloud environments can introduce unnecessary operational complexity.
5. Cost allocation and visibility
Canadia Bank also needed greater visibility into cloud costs and a governance model that could support cost allocation and optimization as cloud adoption expanded.
The Solution: A Secure and Scalable AWS Landing Zone
Canadia Bank and Renova Cloud implemented an AWS Landing Zone as the foundation for the Bank’s cloud transformation journey.
The solution was designed to create a secure, automated, and compliant multi-account AWS environment with:
- Centralized governance and security controls
- Standardized networking
- Centralized logging and identity management
- Automated account provisioning
- Cost governance
- Secure connectivity between AWS and the on-premises environment
The Landing Zone provides a standardized foundation that can support future cloud workloads and broader migration initiatives.
Building a Connected Hybrid Cloud Environment
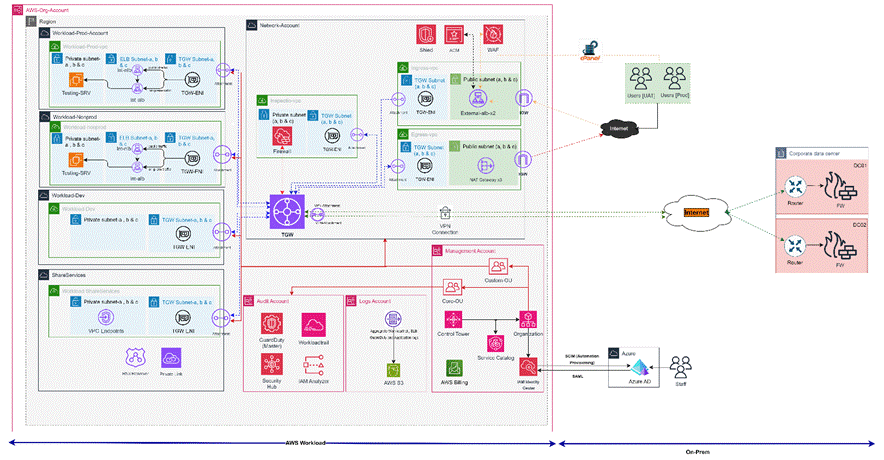
The architecture combines multiple AWS services to establish a controlled and scalable cloud environment.
Centralized network connectivity
AWS Transit Gateway provides a central hub for connecting Amazon VPCs and on-premises networks, reducing the complexity associated with multiple point-to-point network connections.
For private connectivity to the Bank’s on-premises environment, AWS Site-to-Site VPN provides secure internal access.
Network security
AWS Network Firewall provides fine-grained control over network traffic. Together with AWS Firewall Manager, security policies can be centrally managed and applied across VPCs and AWS accounts.
Multi-account governance
AWS Control Tower helps establish and operate the Bank’s multi-account AWS environment with prescriptive controls designed to support security and compliance requirements.
Application and internet connectivity
NAT Gateway enables private resources inside VPCs to access the internet.
Amazon Route 53 provides DNS and routing capabilities, while an Application Load Balancer routes public internet requests to application servers hosted in private subnets.
An external load balancer also supports high availability across two Availability Zones in the production environment.
The AWS Architecture
The implementation brings together networking, security, governance, and application connectivity to create a standardized hybrid cloud foundation.
Key AWS services include:
- AWS Control Tower
- AWS Transit Gateway
- AWS Network Firewall
- AWS Firewall Manager
- AWS Site-to-Site VPN
- NAT Gateway
- Amazon Route 53
- Application Load Balancer
Business Outcomes
The AWS Landing Zone provides Canadia Bank with a stronger foundation for its cloud transformation journey.
| Before | With AWS Landing Zone | Business Impact |
| Cloud adoption without a standardized foundation | Secure and standardized multi-account AWS environment | Creates a structured foundation for future cloud workloads |
| Complex network connectivity | Centralized connectivity through AWS Transit Gateway | Simplifies connections between AWS VPCs and on-premises networks |
| Distributed security controls | Centralized security policies and network controls | Strengthens governance and security enforcement |
| Manual or inconsistent environment provisioning | Automated account provisioning through AWS Control Tower | Reduces operational overhead and improves standardization |
| Limited cost governance | Cost governance and allocation capabilities | Improves cost visibility as cloud adoption expands |
| Dependence on existing infrastructure | Hybrid AWS and on-premises connectivity | Supports a gradual cloud transformation approach |
A Foundation for Future Cloud Migration
The Landing Zone is not the end of Canadia Bank’s cloud journey. It provides the foundation for future phases of cloud adoption and workload migration.
With centralized governance, standardized networking, security controls, and automated provisioning in place, Canadia Bank is better positioned to expand its AWS environment while maintaining consistency across accounts and workloads.
The implementation also supports operational resilience through AWS-managed infrastructure and provides a foundation for disaster recovery and future cloud-native development.
Key Takeaway
Canadia Bank’s cloud transformation starts with a strong foundation.
By implementing a secure and scalable AWS Landing Zone, the Bank established the governance, networking, security, and operational capabilities needed to support its broader cloud adoption journey.
The result is more than a cloud environment. It is a standardized foundation designed to help Canadia Bank migrate workloads, improve resilience, manage costs, and scale its cloud adoption with greater confidence.
From a complex hybrid environment to a secure foundation for cloud transformation.
Ready to Build Your Cloud Foundation?
Cloud transformation starts with the right foundation.
Renova Cloud helps organizations design and implement secure, scalable AWS environments – from cloud foundations and Landing Zones to migration, modernization, security, and managed operations.
Ready to explore what’s possible? → Work with us